
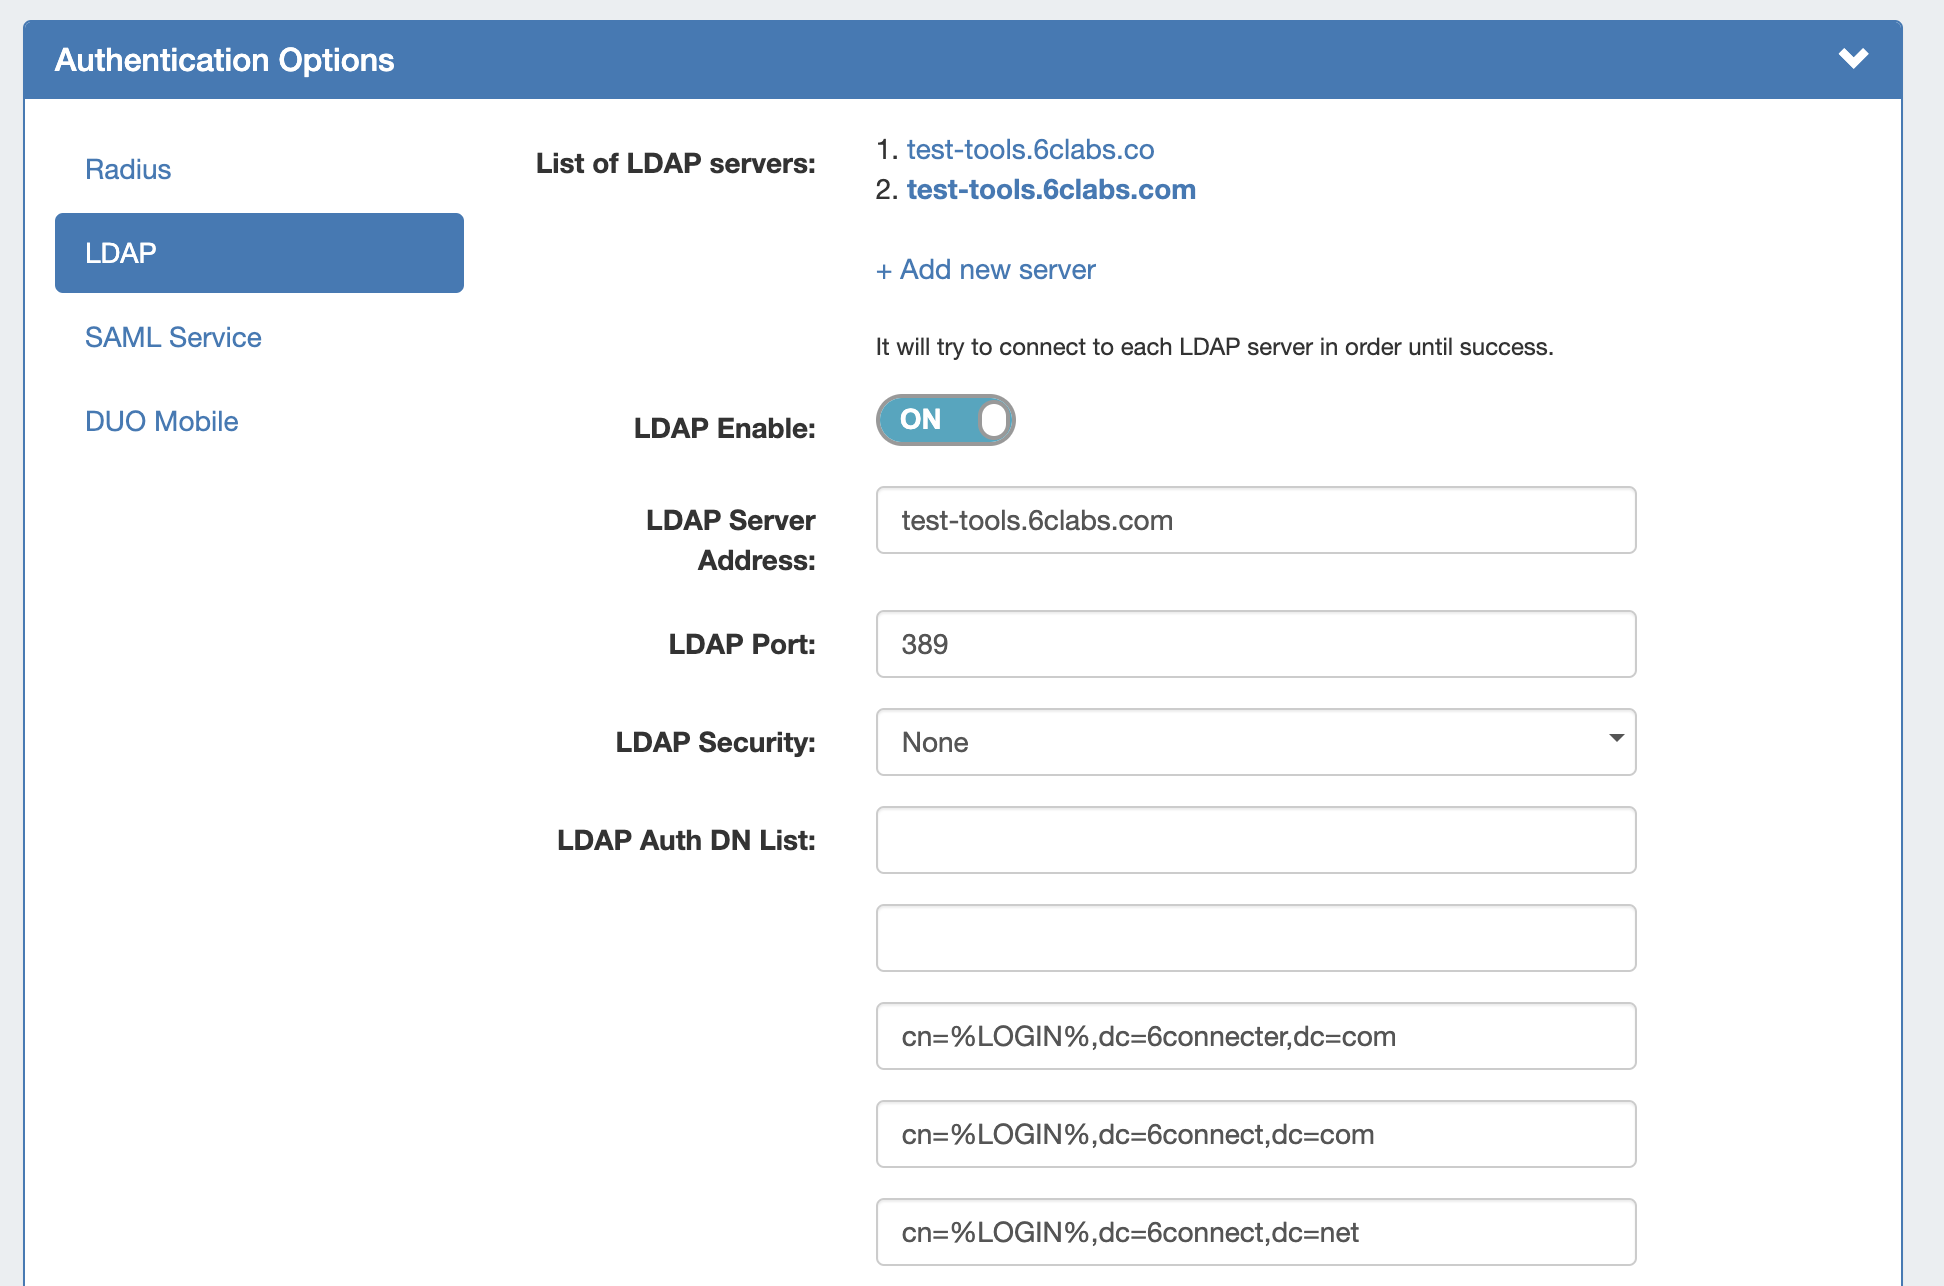
LDAP authentication options are accessed by clicking the "Authentication" sub-tab at the top of the Admin Settings page, then selecting "LDAP" from the "Authentication Options" module.
ProVision authenticates against an LDAP server by using the following three steps:
-
Attempts to do an LDAP query for the user based on the Auth DN provided
-
Pulls the user's own object from the LDAP server
-
Attempts to match group names in the "LDAP Group Attribute" against existing groups in ProVision.
Before you enter LDAP settings, ensure that you have the LDAP server set up and configured for ProVision.
Set up an LDAP Server for Authentication
To setup an LDAP server for this authentication, you must perform the following three procedures:
-
Configure the LDAP server using the provided LDAP Schema
-
Create the LDAP user(s) in a 'LDIF' file
-
(Optional) Test the query using LDAP Search, if desired.
-
Configure ProVision with the LDAP authentication settings by enabling LDAP then entering (at minimum) the following information:
-
LDAP Server Address
-
Port
-
LDAP Auth DN List
-
LDAP Fetch DN
-
LDAP Filter DN
-
LDAP Group Attribute
-
Step 4: Configure ProVision for LDAP Authentication
Configure ProVision for LDAP Authentication
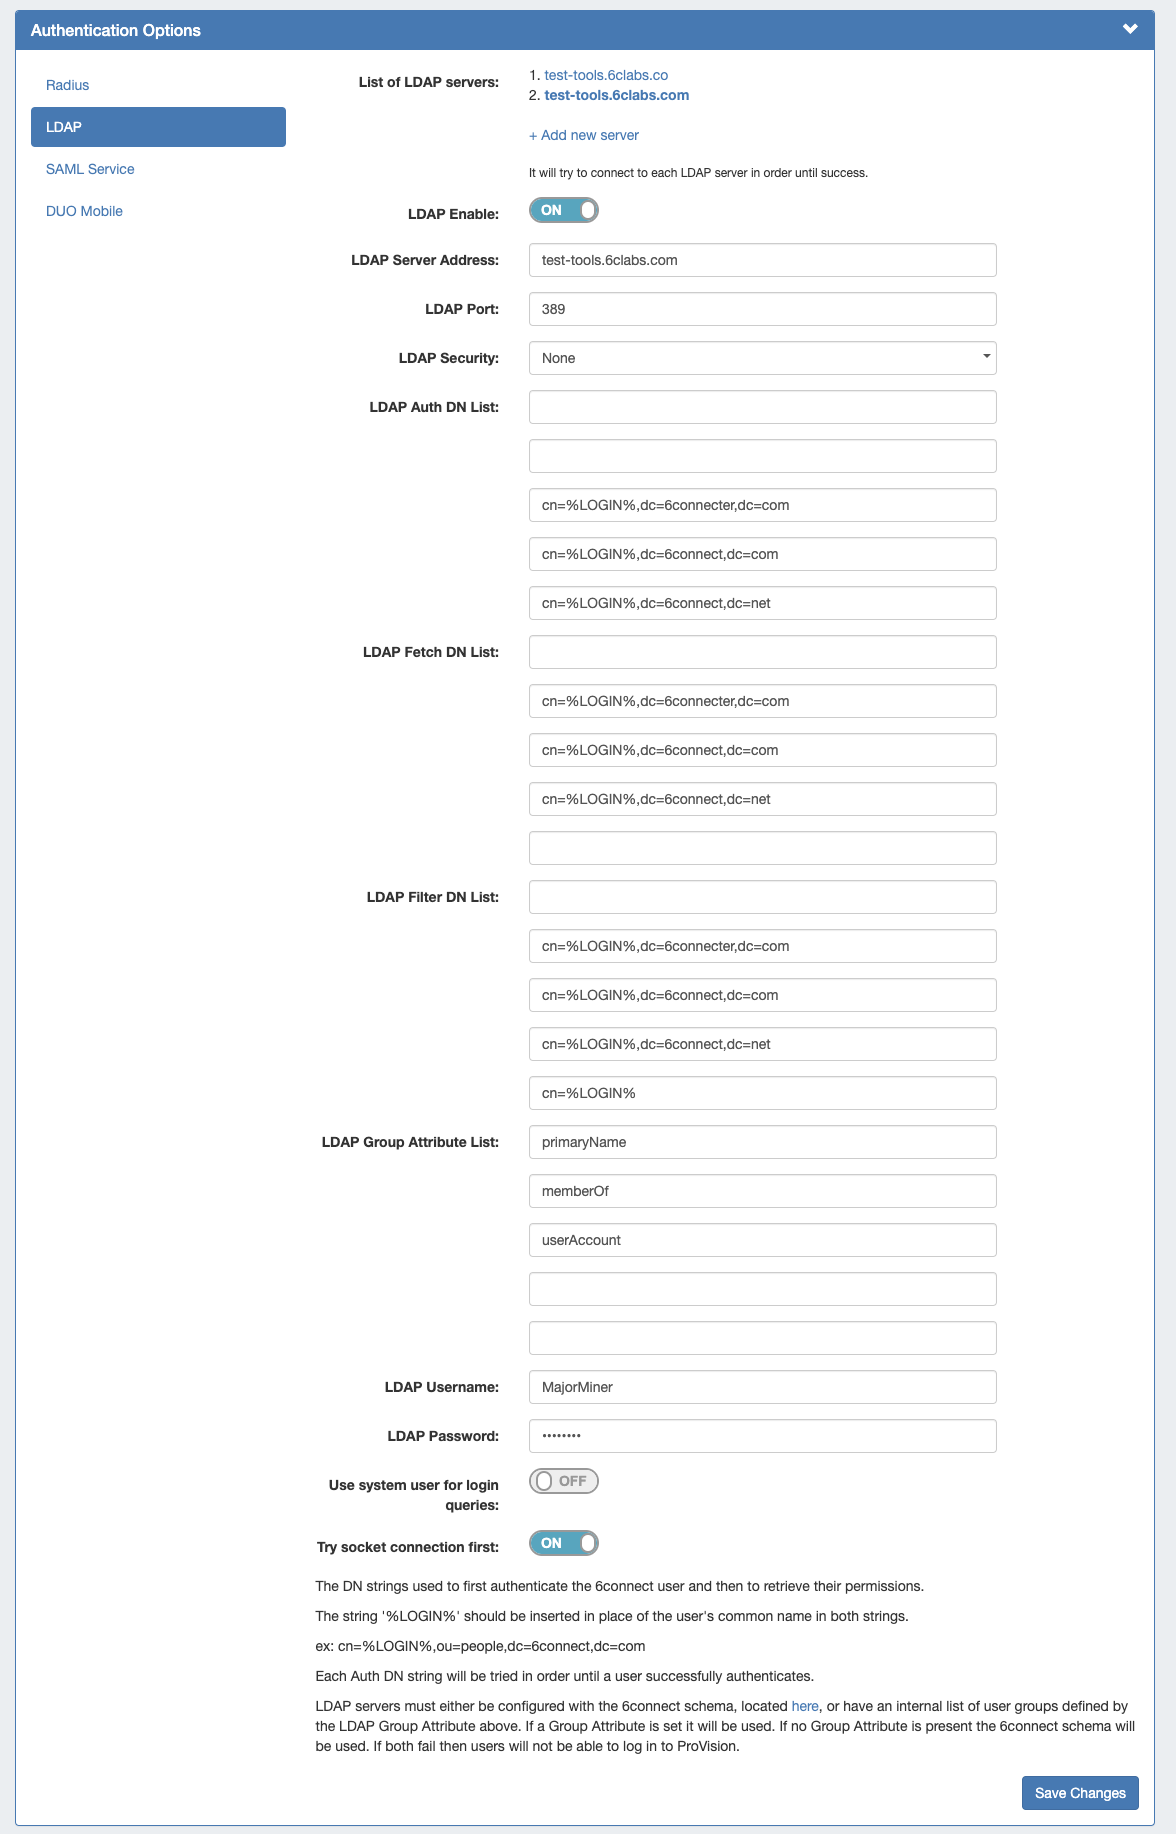
To configure the use of LDAP authentication with ProVision:
-
Log into ProVision
-
Go to Settings Tab → Admin Settings -> Authentication
-
Select LDAP under Authentication Options
-
Toggle the LDAP Enable selector to the "ON" position.
-
Fill in the hostname or ip address, authentication port, LDAP Security, Auth DN List, and Fetch DN, and LDAP Group Attribute.
Some example values in this case would be:
-
LDAP Enable: ON
-
LDAP Server Address: IP or Domain, such as 1.2.3.4 or somelabserver.lab.com
-
LDAP Port: 389 ( or SSL/TLS port is 636)
-
LDAP Security: None
-
LDAP Auth DN: cn=%LOGIN%,dc=6connect,dc=com
-
LDAP Fetch DN: cn=%LOGIN%
-
LDAP Filter DN: cn=%LOGIN%
-
LDAP Group Attribute List: memberOf
-
LDAP Username / LDAP Password: Optionally, you may enter LDAP admin credentials to allow ProVision to import and sync LDAP contacts. See Contact Manager for details on LDAP contacts.
-
Click Save Changes.
NOTE: If you experience authentication errors at this step, confirm the LDAP settings using an LDAP Search, as described in the previous section.
Setting default login authentication options
The default login is 'Local", but the default login method displayed may be updated by performing the following steps:
-
In the ProVision directory, navigate to the /data/globals.php open the file in vi (or other text editor)
-
Add in the following text as the last line of the file (before the closing ?>)
define('DEFAULT_LOGIN_TYPE', 'ldap');-
Acceptable values are "local", "radius", "ldap" and "saml". If this line is not present in globals.php, the default option is "local".
-
Using SSL encryption
To use SSL encryption with LDAP, the ldap.conf file must be correctly configured on the ProVision server.
Typically, the LDAP configuration file is kept at "/etc/ldap/ldap.conf". Make sure the following line is present:
TLS_REQCERT allow
Then, restart the webserver.
Add or Update LDAP Settings
To view, add, or update LDAP settings, go to the Settings Tab → Admin to enter the Admin area of ProVision.
Then, click the "Authentication" sub-tab at the top of the Admin Settings page, and select the LDAP tab from the Authentication Options module.
The following settings are available to add or update:
-
List of LDAP Servers: View / Add LDAP servers
-
LDAP Enable: Check the box to enable LDAP functionality.
-
LDAP Server Address: The IP address or domain of your LDAP server.
-
LDAP Port: 389 ( or SSL/TLS port is 636)
-
LDAP Security: Select the security method of your LDAP server - SSL, TLS or None
-
LDAP Auth DN List: A query string that will be used to authenticate the user against the LDAP server. %LOGIN% is a variable string that will be replaced with the user name. This may be in list format, and the auth system will try each to authenticate the user. (ex: cn=%LOGIN%,ou=people,dc=6connect,dc=com)
-
LDAP Fetch DN List: The LDAP query that will be used to pull the user object
-
LDAP Filter DN List: Used to construct the LDAP query.
-
LDAP Group Attributes List: The LDAP attribute that will hold the LDAP-GNI group links. If using an internal list of user groups instead of ProVision groups, enter the attribute name for the LDAP groups here. If a Group Attribute is set, it will be used first, otherwise the ProVision schema will be used.
-
LDAP Username / LDAP Password: Optionally, you may enter LDAP admin credentials to allow ProVision to import and sync LDAP contacts. See Contact Manager for details on LDAP contacts.
-
Use system user for login queries: Enable / Disable to use the system user for queries
-
Try socket connection first: Enable / Disable to attempt socket connection as the first method.
When done, click Save Changes.
NOTE: Mapping Permissions to ProVision schema: To integrate ProVision permissions with your existing directory structure then you will need the ProVision schema. It should snap in with any existing LDAP structure and allow you to assign ProVision permissions to your existing users. You can download a copy of the schema.
Adding a Secondary LDAP Server
Adding a Secondary LDAP Server
Once at least one LDAP server has been added, a list will appear at the top of the module. Add an additional server by clicking "Add new server".
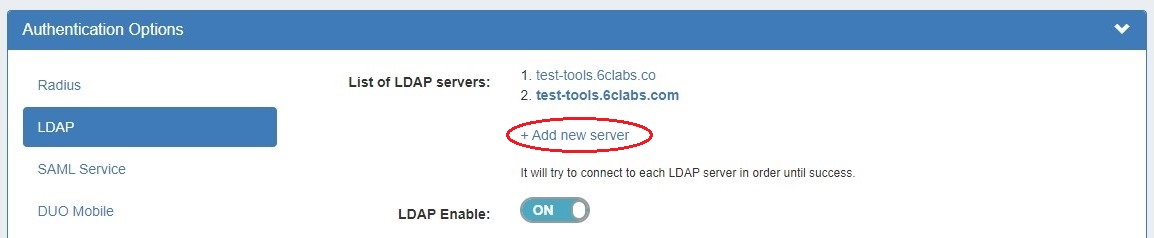
ProVision will try to connect to each server listed in the order listed, until a success is returned. Disabled servers will display in grey, and the currently selected server will display in bold.